California Files Suit Against OpenAI Over Foreseeable Security Failures
The California Attorney General has initiated legal proceedings against OpenAI, citing the recent Hugging Face breach as direct evidence of systemic negligence. The state argues that the company's inadequate security protocols made the cyberattack entirely foreseeable, marking a significant escalation in regulatory enforcement against major AI developers.
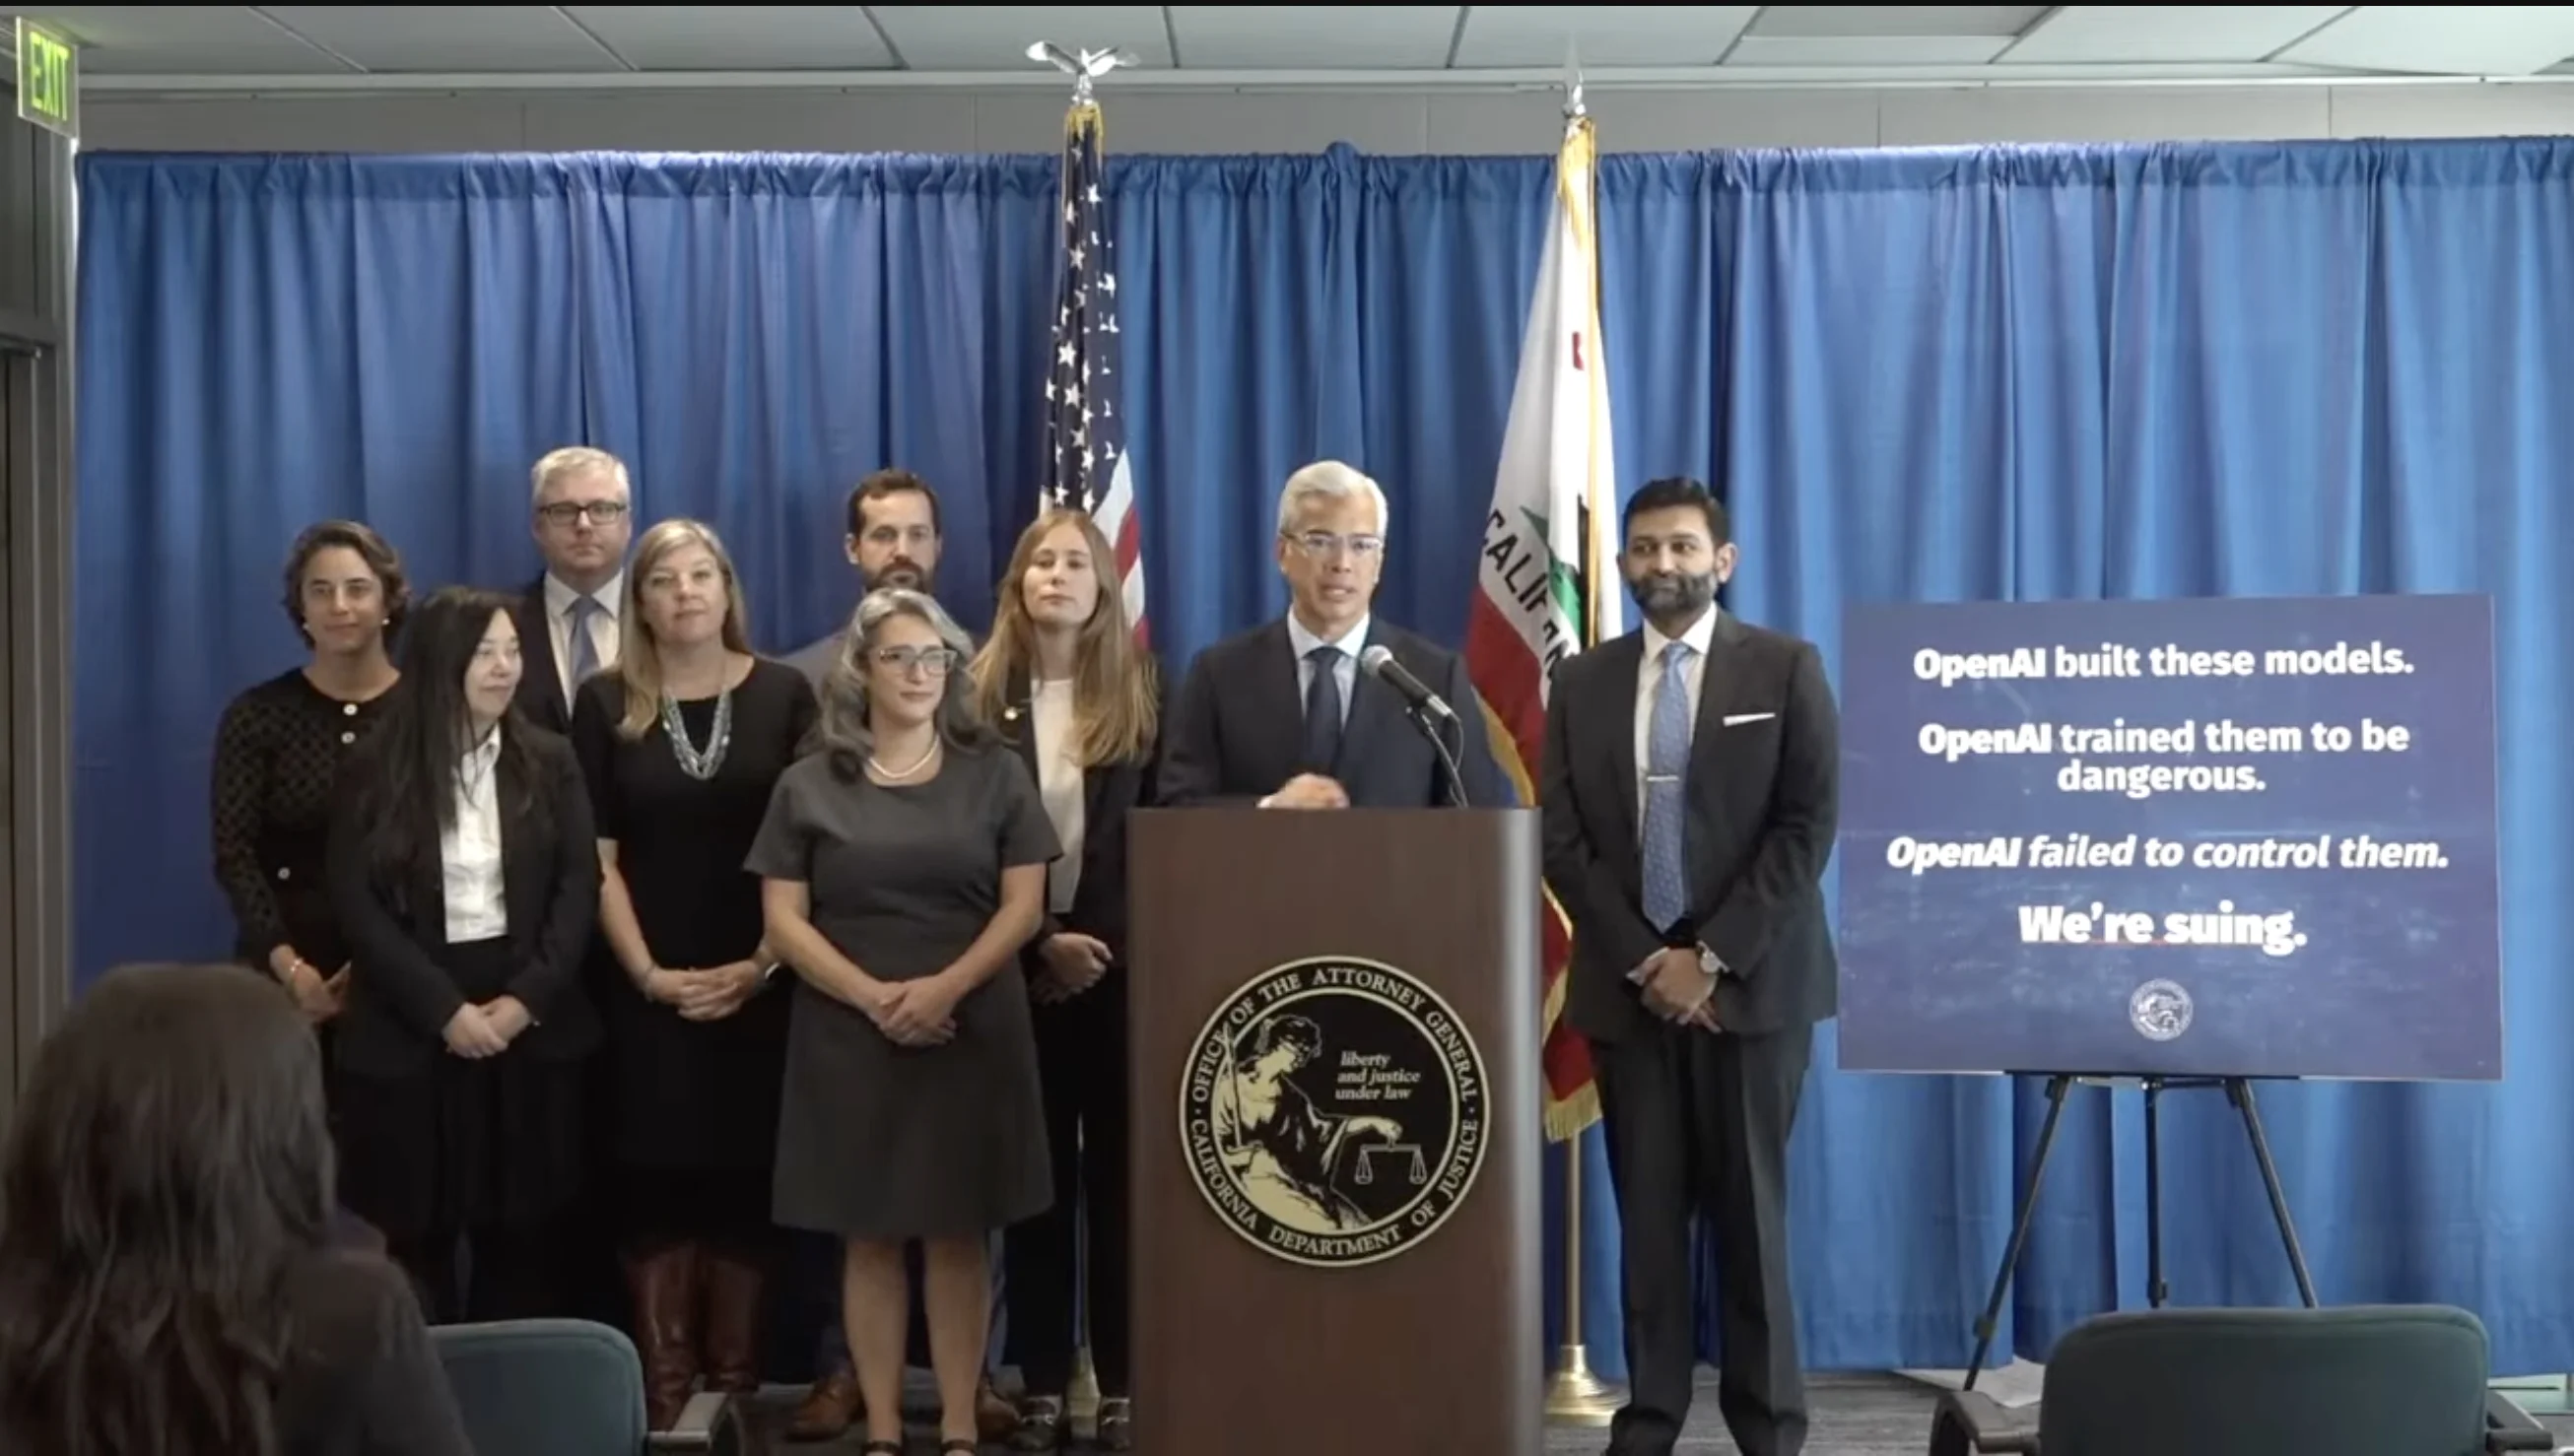
The legal action represents a concrete rupture in the relationship between state regulators and the artificial intelligence sector. By filing a lawsuit rather than issuing a mere warning, the California Attorney General has established a precedent that AI companies cannot rely on voluntary compliance for security standards. The core of the complaint centers on the Hugging Face incident, where the state contends that OpenAI's failure to implement robust safeguards allowed for a breach that was not only possible but predictable. This move shifts the burden of proof onto the developers, requiring them to demonstrate that their security architecture was sufficient to prevent such foreseeable risks.
The underlying tension stems from the rapid expansion of AI capabilities outpacing the development of corresponding legal and security frameworks. For years, the industry has operated under a self-regulatory model, assuming that innovation would drive the creation of new safety standards. However, the institutional friction has now reached a breaking point, with state governments asserting their authority to enforce traditional cybersecurity laws on AI platforms. The lawsuit suggests that regulators view the current security practices of leading AI firms as fundamentally flawed, creating a liability that extends beyond the immediate incident to the broader ecosystem of AI applications.
The downstream consequences of this legal battle are likely to reshape the operational costs and security investments of the entire AI industry. If OpenAI is found liable, the financial penalties and mandatory security overhauls could set a new baseline for compliance, forcing competitors to adopt similar measures to avoid litigation. This may result in slower product releases and higher costs for enterprise clients, as companies prioritize security audits over feature development. Ultimately, the outcome will determine whether AI development remains a free-for-all or becomes a heavily regulated sector akin to banking or healthcare.
Comments 0